A week of outages from Microsoft to the FAA had separate causes and a shared weak spot
Officials say no attack tied the failures together. Their explanations point to rushed updates, aging hardware and a few platforms that much of daily life depends on.
 By Aisha Morgan
· 6 min read
Key Takeaways
- One analysis rates the stretch that began Nov. 12 as the worst run of major outages since August 2013.
- The causes cited so far are ordinary ones: server bugs, overloaded legacy equipment, a software bug and botched updates.
- Security experts say AI-driven vulnerability hunting is pushing companies to patch faster than they can safely test.
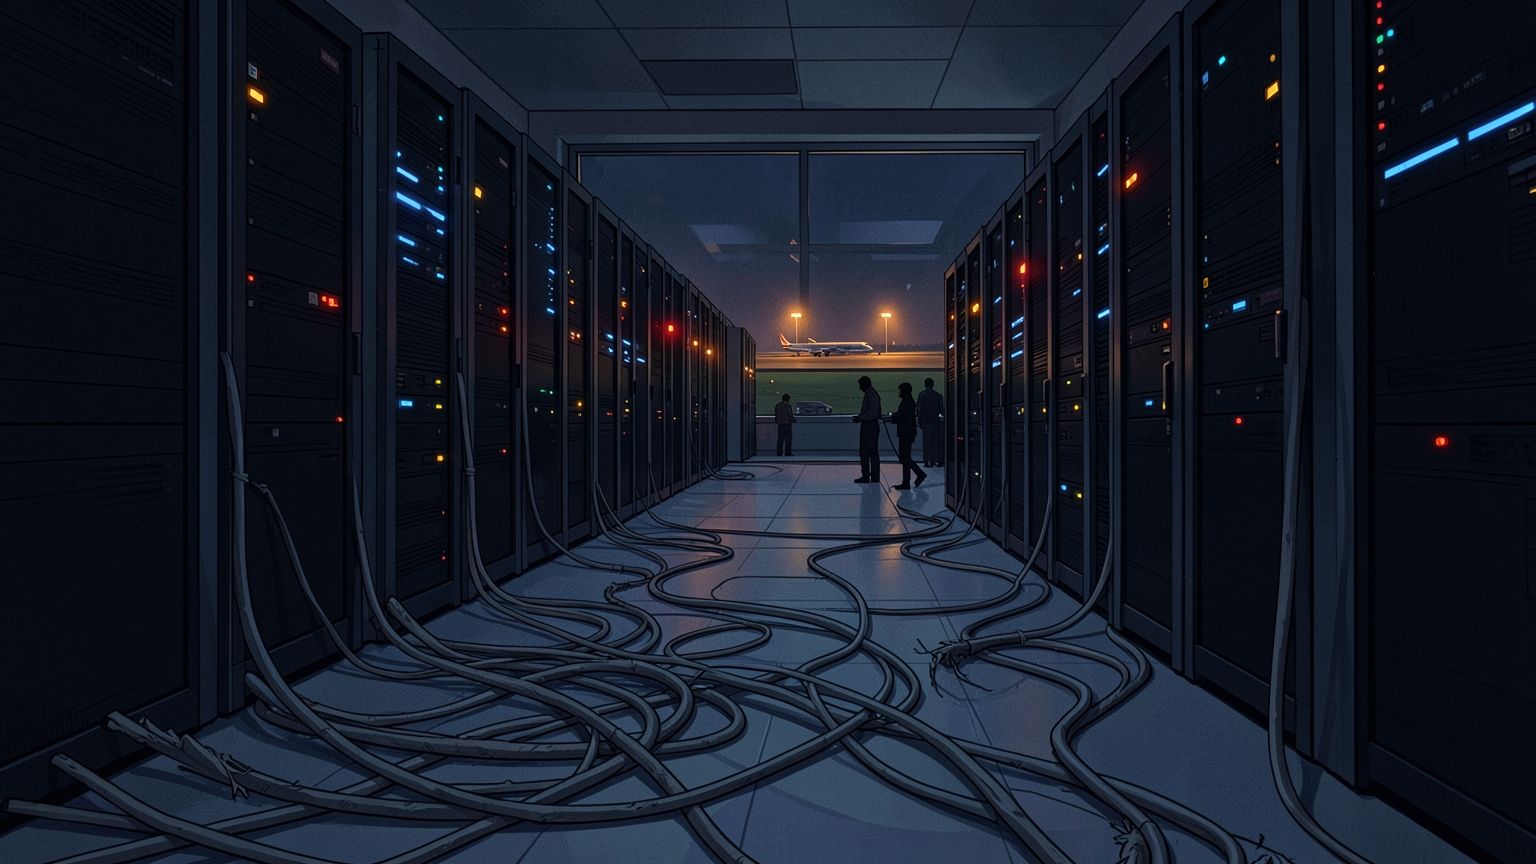
The string of failures that took down Microsoft's Outlook and Teams, stopped departing flights across the country and disrupted payments at JPMorgan Chase was not a coordinated attack, according to the companies and agencies involved. The explanations they have given so far point to something duller and possibly harder to fix: hurried changes landing on aging systems that a huge number of everyday services depend on.
The run began Nov. 12 with a lengthy Microsoft 365 disruption that hit Outlook and Teams. The Federal Aviation Administration then ordered a nationwide halt to departing flights that lasted more than four hours. United Airlines had a separate technology failure that delayed more than 100 flights. JPMorgan Chase had payment problems that were separate from a recent cyberattack. The National Security Agency's classified internal network went down. An internal Apple update knocked out iCloud and Apple Pay, and Marriott's hotel network had problems too.
Several of those incidents were serious on their own, including a rare nationwide ground stop. Packed into roughly a week, they looked like a pattern, and the numbers suggest the impression was not just imagined.
How unusual the week really was
Rohit Krishnan, an AI researcher at the University of Pennsylvania's Wharton School, mined outage data and concluded that the stretch was likely the worst sequence of major tech failures since August 2013. He also cautioned that the totals were high but not unprecedented, and that recency bias drives much of the alarm.
Downdetector's figures point the same way. Luke Kehoe of Ookla, which owns the site, told Mashable that Americans filed nearly 6 million reports in the seven days ending Nov. 16. That was more than in any other week of the previous 12 months. The number of services flagged with problems was higher than in all but a few weeks of that period.
That is a useful corrective. A bad week is real, but one week is too small a sample to show that something has changed in how often systems fail. The stronger evidence is about how far each failure spreads, and that is where the story gets more interesting.
What broke, system by system
Put side by side, the official causes have little in common. Microsoft pointed to server bugs. The FAA's trouble came from legacy equipment that was overloaded, and the failure has been traced to networking gear. JPMorgan Chase blamed a bug in on-premises software. The NSA's disruption followed scheduled maintenance and security patches. Apple's came from an internal software update that went wrong.
Microsoft's case may be the most telling. According to WIRED executive editor Brian Barrett's account on the outlet's podcast, the trigger was a change pushed out in July that sat dormant until a later update set it off. Microsoft has published a shorter postmortem and plans a fuller one. A flaw that waits four months to fire is exactly the kind of risk that fast, layered deployments create, and it is hard to catch in testing.
The FAA failure shows the other half of the problem. Anusha Iyer, a software engineer who founded the security startup Corsha, told TechCrunch that preliminary findings suggest the agency was modernizing its telecommunications infrastructure when the new equipment overwhelmed older hardware that could not keep pace. In her view, the culprit was a rushed blend of old and new systems rather than AI itself.
"The fault is the rushed mix of the legacy and modern systems," Iyer said.
Government officials have played down any common thread. Secretary of State Marco Rubio said there was "zero evidence" the outages were connected, and the director of national intelligence said they did not appear tied to state-sponsored terrorism.
Where AI fits in
Public suspicion fell quickly on hackers, AI or both. That instinct has some recent fuel. A wave of unrelated security incidents on Oct. 21, which some in the industry called "Black October," hit projects including PHP, Node.js and LiteLLM. In recent weeks, hackers in France also attacked refrigerators in a grocery store and a blood bank.
The experts quoted across the coverage mostly reject the idea that AI agents went rogue. They describe a more indirect role. Gunter Ollmann, chief technology officer at the security firm Cobalt, told TechRadar that the industry is still dealing with the aftermath of a "Mythos moment" in April, when AI showed it could find vulnerabilities at enormous scale. Security teams used to test updates and roll them out gradually, he said, but "now they simply don't have that luxury" because attackers use the same tools.
Dave DeWalt, a longtime cybersecurity executive who once ran McAfee, made a similar case to TechCrunch. He described the outages as likely the "growing pains of a security system that's getting stronger, not weaker." Old flaws are surfacing faster than ever, and companies are racing to close them before anyone can exploit them. "That surge in patching is disrupting things in the short term," DeWalt said.
Steve Povolny, who leads AI strategy and security research at Exabeam, put the human role plainly. The likelier failure, he said, is someone using an AI tool to move faster, or an automated change shipped without enough review. "Either way, a person is at the controls," he said.
That framing is more useful than either blaming AI outright or clearing it entirely. None of the causes cited so far involves AI directly. But if AI is forcing companies to patch faster than their testing can handle, it shapes the conditions in which ordinary mistakes happen. The Microsoft change that lay dormant since July fits that picture better than any hacker theory does.
A few platforms underneath everything
The other thread tying these incidents together is structural. Findlay Whitelaw, field chief information security officer at Exabeam, told TechRadar that a small set of cloud, identity and payment platforms supports a large share of the services people use daily. When one of them falters, many users notice at the same moment, and the episode gets read as a wave. She added that "the timing alone doesn't establish a common cause or a coordinated attack."
Povolny made a related point: services that look unrelated often rely on the same cloud providers, DNS, certificates and networking vendors. Banking shows how this works. JPMorgan Chase's problem rippled outward because banks act as counterparties to one another.
David Wang, chief operating officer at the AI gateway company Tetrate, argued that dependence on AI tools makes the stakes higher. When a service like Copilot goes down, he told TechRadar, work stops across a business. "Whether outages are becoming more frequent is hard to say, but the impact of each one is growing," Wang said. His advice for organizations was blunt: "I'd plan for more disruption, not less."
That seems like the right reading. The failures in this cluster were not exotic. They were bugs, overloaded equipment and botched updates, the kind of thing that has always happened. What has changed is how much rides on a handful of systems and how little time teams now get to test changes before shipping them. Grounded flights, failed transfers and unreachable inboxes come from the same pressure.
Not everyone sees cause for alarm. Mieke Verburgh, a senior director at Malwarebytes, told TechRadar that the incidents call for attention rather than panic. Most of the problems have known fixes, she said: test updates before rollout, keep reliable backups and tighten security overall.
Those fixes are familiar, and that is the uncomfortable part. Every lesson from this week was already known. The test now is whether companies under pressure to patch at AI speed will slow down enough to apply them.
Sources
Aisha Morgan
Aisha Morgan covers software, digital services, and the product updates that change everyday technology use. Her work follows new features, platform decisions, and the details within release announcements. She explains what has changed, who may be affected, and how individual updates fit into broader shifts in the software landscape.
View all stories